Ethical hacking’s main goal is to find a system’s flaws or vulnerabilities and secure it against hackers. Hackers are always attempting to get unauthorized access to an organization’s resources to gain undeserved profits.
When a company wishes to do offensive testing to uncover system flaws, they call it “ethical hacking.” The individual doing the testing is known as an ethical hacker. They carry out the same operation on the system as a hacker, but in a more ethical manner. Nowadays, ethical hacking is a thriving profession.
From our partners:
It can apply to a variety of organizational domains, including networks, network devices, network protocols, online applications, web technology, and cloud computing. To understand ethical hacking, researchers must master all of the domains listed above. Thereafter, the ethical hacker needs to focus on the domain in which they want to specialize. For example, if someone wants to test a web application, they must learn everything about it.
Basics Needed to Be an Ethical Hacker:
HyperText Markup Language/ HTML
It’s used to show pages in a web browser. Most websites utilize HTML as their frontend, so understanding how content is rendered is critical. This is why it is crucial to learn HTML when you first begin.
Script
Scripting is a code snippet used to make a website more user-friendly. The script plays an important part in the development of web applications for automation and validation. Mostly, Javascript is used. It’s critical to understand how the scripts are put into action.
Networking
Ethical hackers must understand basic network topology — how network devices work, what hazards they may contain, what a device’s job is, and how to use it effectively. A person who understands how a product works can try to secure the devices in the same way.
Linux
Most tasks are very easy on Linux instead of Windows, and most servers run on Linux as well. This makes this OS a piece of essential knowledge for ethical hackers. You should be familiar with the Command Line Interface of the OS as well as basic commands like listing, deleting, or modifying files in the Linux CLI environment.
You can easily move on to learning more about the vulnerabilities that an application may have once you’ve gathered the basic knowledge. The Open Web Application Security Project (OWASP) is an online community that offers security-related principles, approaches, documentation, tools, and articles.
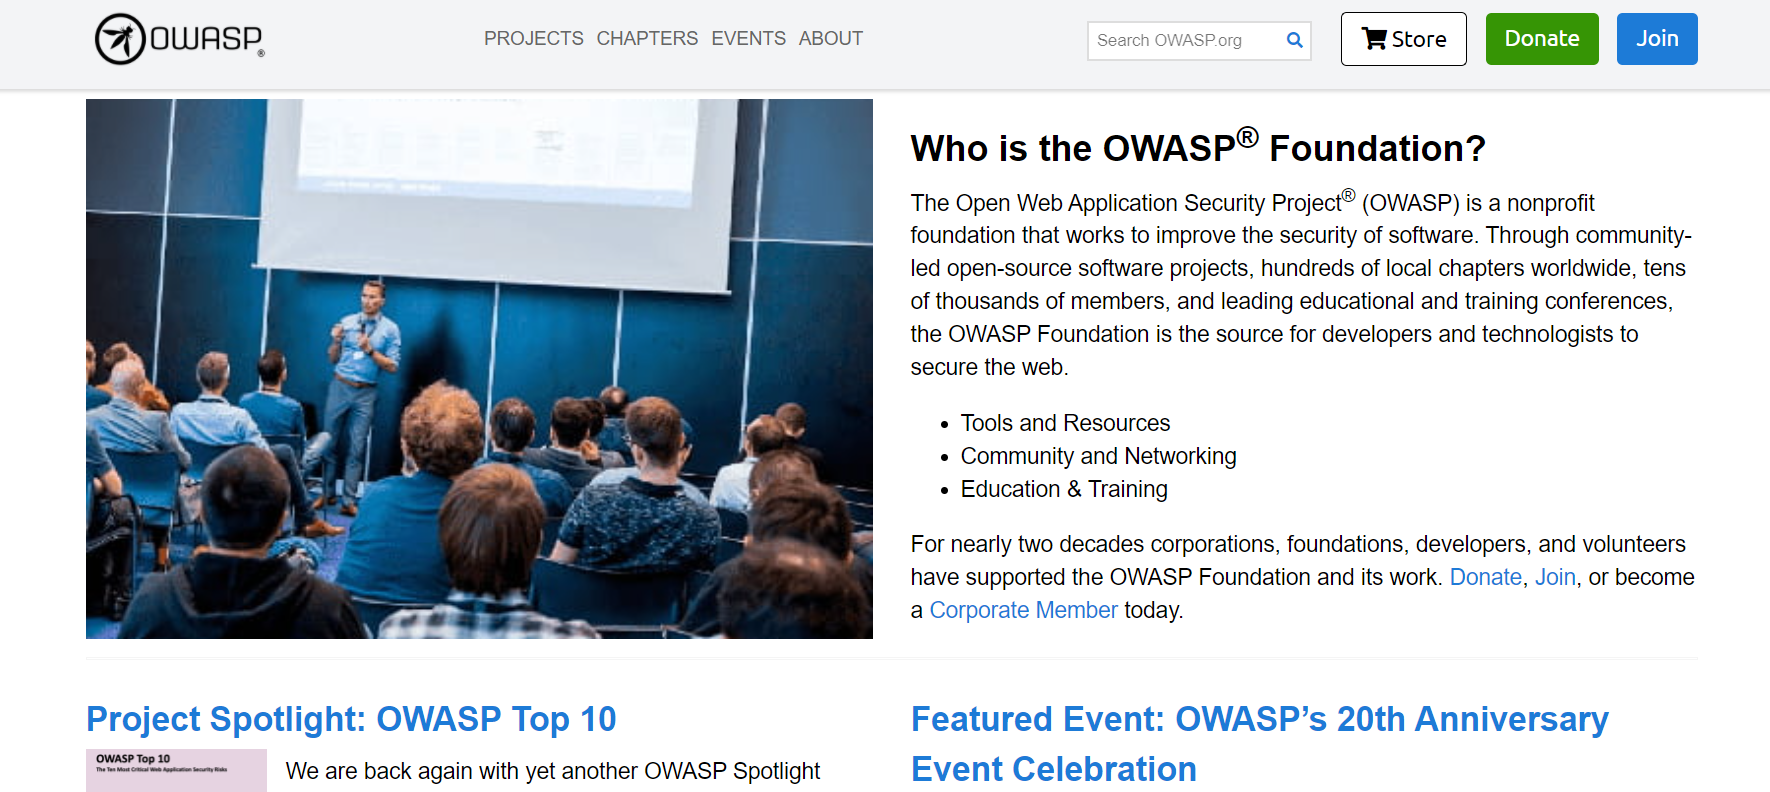
It develops a fundamental understanding of security, and many organizations use it as a guide to implementing security in their own operations. Injection, broken authentication, sensitive data exposure, XML external entities, broken access control, and so on are among the OWASP Top 10 list of vulnerabilities maintained by this project, with severity ranging from 1 to 10. You will find a lot of vulnerabilities, their detection, and remediation in the OWASP list. They also have some examples of vulnerable applications you can use to test your skills and knowledge. You can follow their cheatsheet to learn more about the testing and exploitation of the vulnerability.
How to Keep Yourself Regularly Updated
Cyber security and ethical hacking is a daily moving field, so it is very important for a person to actually keep himself/herself updated. There are a couple of ways that anyone can use to keep them up-to-date with the vulnerabilities research and other stuff that may be disclosed in the field of cybersecurity or ethical hacking.
READ MORE: [button style=’accent’ url=’https://news.aster.cloud/2020/03/19/5-ops-hacks-for-sysadmins/’ target=’_blank’ arrow=’true’ fullwidth=’true’]5 OPS HACKS FOR SYSADMINS[/button]
[button style=’accent’ url=’https://news.aster.cloud/2019/12/06/is-anything-ever-forgotten-online/’ target=’_blank’ arrow=’true’ fullwidth=’true’]IS ANYTHING EVER ‘FORGOTTEN’ ONLINE?[/button]
Read Research by Other Hackers
Nowadays, every researcher publishes a blog about their research. Additionally, some bug bounty platforms make their reports public so that they can be used as a reference to find other vulnerabilities in the system. These two avenues provide much information about the latest trends and updates in the sphere.
Be Knowledgeable About Vulnerabilities and How to Test Them
It distinguishes you from the competition when it comes to exploiting targets. You can do so by participating in company-sponsored CTFs, solving Hackthebox boxes, and much more.
Exploitation Methods
Make your exploitation methods by using best practices as a foundation. Think outside the box to successfully bypass the logic implemented in the code and hunt for business logic vulnerabilities.
Inspect the Target
Always properly inspect the target before moving on to the vulnerability. As you grow more familiar with the system’s features, it will become easier for you to take advantage of it.
Collect Information
Collect as much information as possible, whether active or passive. Some main domains are limited while others are not. Also, by reading security-related news on a dedicated platform, users may learn how hackers exploit real-time vulnerabilities and what enterprises need to do to defend their infrastructure.
Bug Bounties
Participate in bug bounty programs like HackerOne, Syanck, or Cobalt. Many organizations offer their bug bounty programs on platforms, making it simple to practice and try to find vulnerabilities there.
Conclusion
“Practice makes perfect,” as we all know, and as we are practicing to learn and acquire new abilities in the field of ethical hacking, we need to put in the work. Second, always hack ethically. Otherwise, you’re committing a legal offense against the law and the company. Be a hacker with a conscience. Third, all of the above measures will undoubtedly aid in the acquisition of information. However, a good or pro user is one who combines programming and security. So, while you’re learning to program, attempt to learn something else at the same time. Programming is not required, but it enhances your abilities.
This feature was republished from hackernoon.
For enquiries, product placements, sponsorships, and collaborations, connect with us at [email protected]. We'd love to hear from you!
Our humans need coffee too! Your support is highly appreciated, thank you!